← Back to Submind

Topic

malware analysis

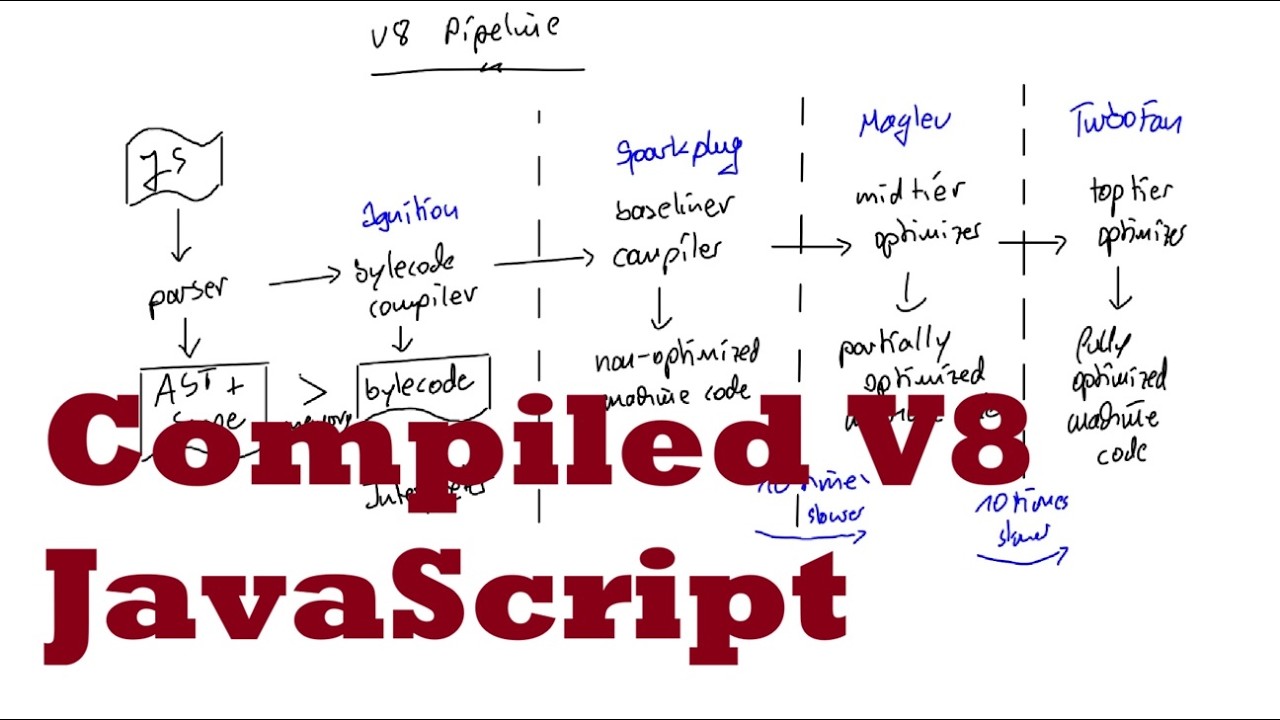
Compiled JavaScript - V8 compilation pipeline and Bytenode

MalwareAnalysisForHedgehogs

The video introduces the V8 compilation pipeline and its relevance to analyzing modern malware that utilizes Electron frameworks or packaged executables containing protected JavaScript code. In many cases, developers distribute only bytecode rather than source code to hinder reverse engineering, mak …

Malware Analysis - PoisonX rootkit, Kernel driver rootkit markup in Ghidra

MalwareAnalysisForHedgehogs

The video provides a detailed walkthrough of analyzing the PoisonX rootkit kernel driver using Ghidra to reverse engineer its malicious functionality. The presenter begins by explaining that while many drivers use obfuscation techniques like packing or encryption, this specific sample has a relative …